



An actively maintained fork of Gophish, the open-source phishing toolkit.
Gophish is a widely used, battle-tested
toolkit for running phishing simulations and security awareness training.
Unfortunately, upstream gophish/gophish has had no commits since
September 2024, go.mod still requires Go 1.13, and several of its core
dependencies carry known CVEs — not great for a tool that security teams
run inside their own networks.
This fork exists to keep that foundation solid, and to fill the gaps that show up when a team runs it. So far that's meant:
- Dependency & toolchain modernization: Go 1.13 → 1.26+, a full
migration off the long-abandoned
jinzhu/gorm(v1) togorm.io/gorm(v2), the unmaintainedbitbucket.org/liamstask/goosereplaced with the actively maintainedpressly/goose, and every dependency brought current.govulncheckfindings went from 47 reachable vulnerabilities down to a single one with no upstream fix yet available. - Real, verified security fixes found along the way: a stored XSS in
the campaign delete dialog, a crash that could take down the whole
process (not just one request), an SSRF-adjacent bug where configuring
allowed_internal_hostssilently blocked all external traffic instead of just internal ranges, and an authorization bypass letting a locked-out user unlock their own account via their still-valid API key. - A rebuilt, minimal frontend toolchain: Gulp + Webpack (18 npm
packages, two build systems quietly stepping on each other) replaced
with a single
esbuildscript. - CI that actually catches things:
govulncheck, linting, and automated dependency updates, none of which upstream had. - Features upstream lacks: teams, so several operators share the same campaigns and assets instead of each working in their own silo; a read-only auditor role for reviewers and clients; OAuth 2.0 for IMAP reporting; SMTP CC and per-profile send rates; tags for categorizing and filtering templates, landing pages, sending profiles, groups, and campaigns; and anonymous campaigns that permanently scrub recipient data for privacy-sensitive reporting.
Every change here is tested and verified against a running instance, not just "looks right." See CONTRIBUTING.md for how this fork is maintained and SECURITY.md for reporting vulnerabilities.
- What is Gophish?
- Install
- Building From Source
- Docker
- Setup
- Quick Start
- Documentation
- Issues
- Contact
- License
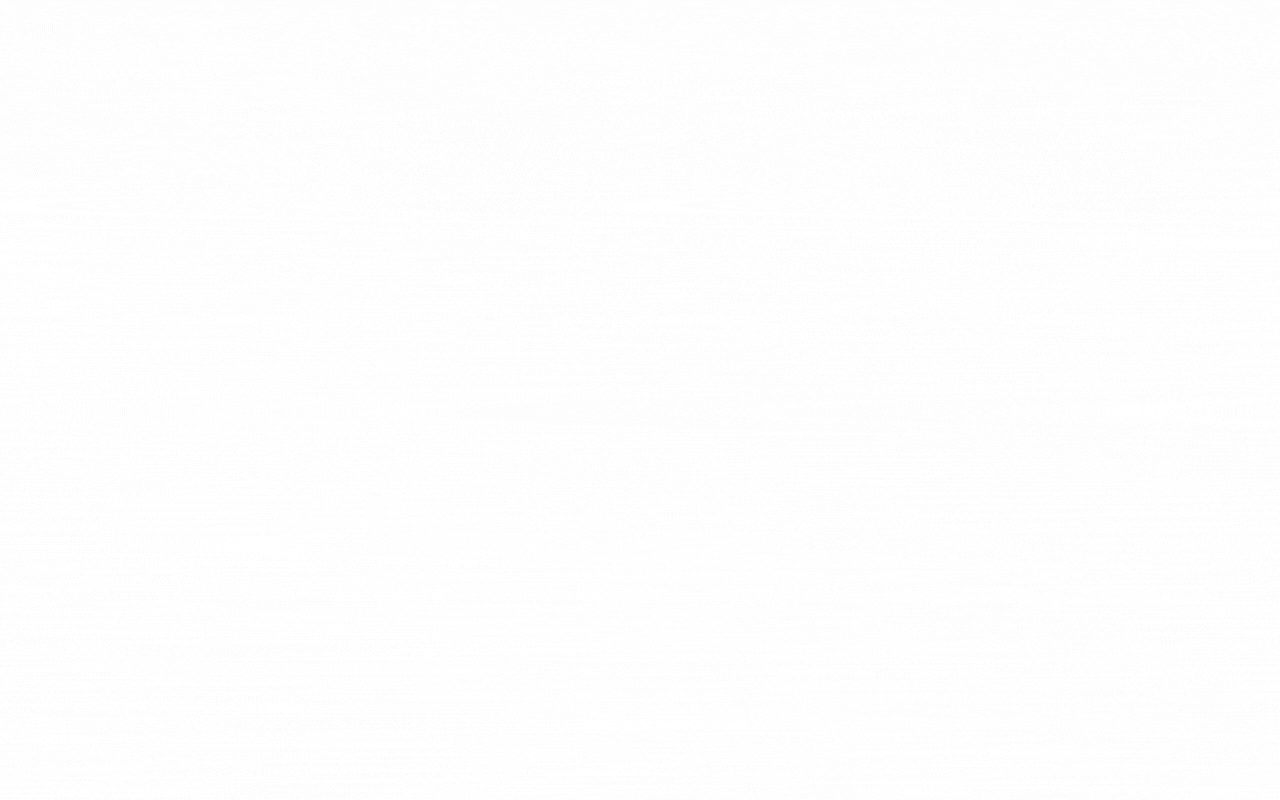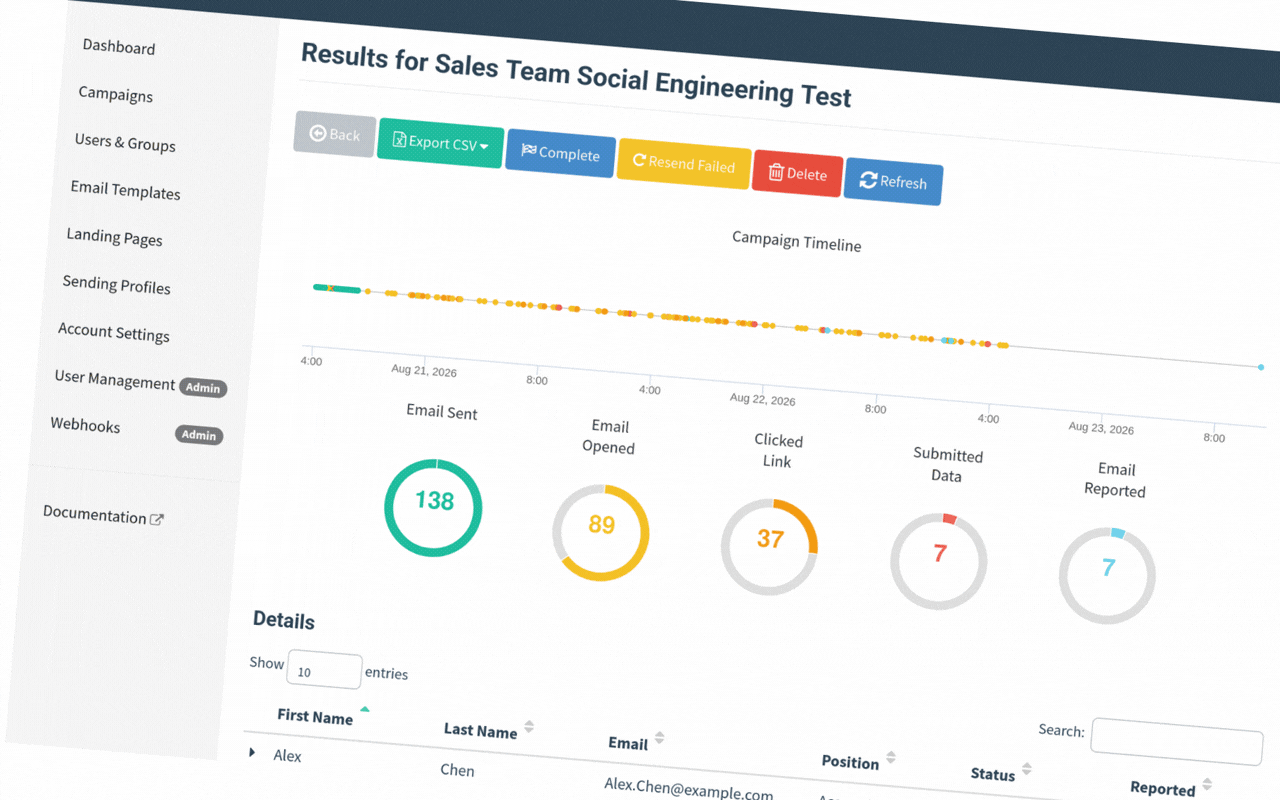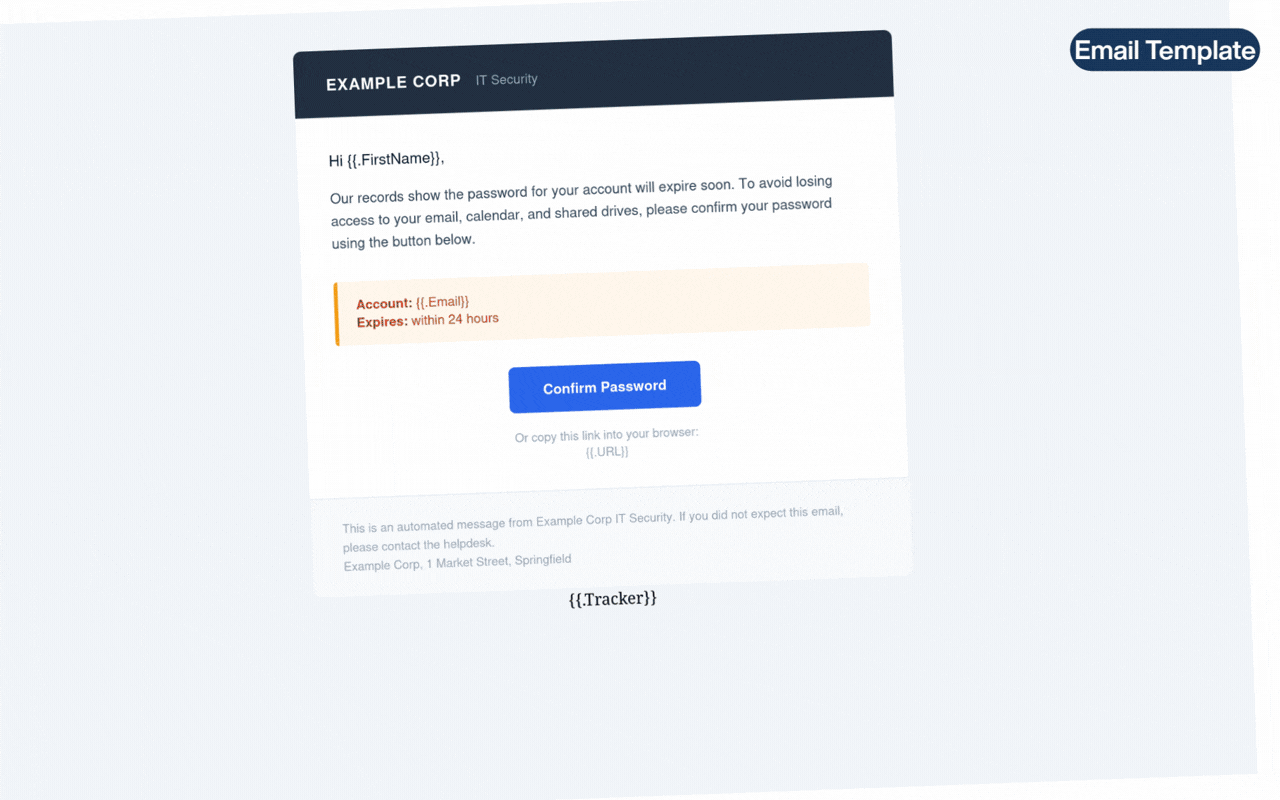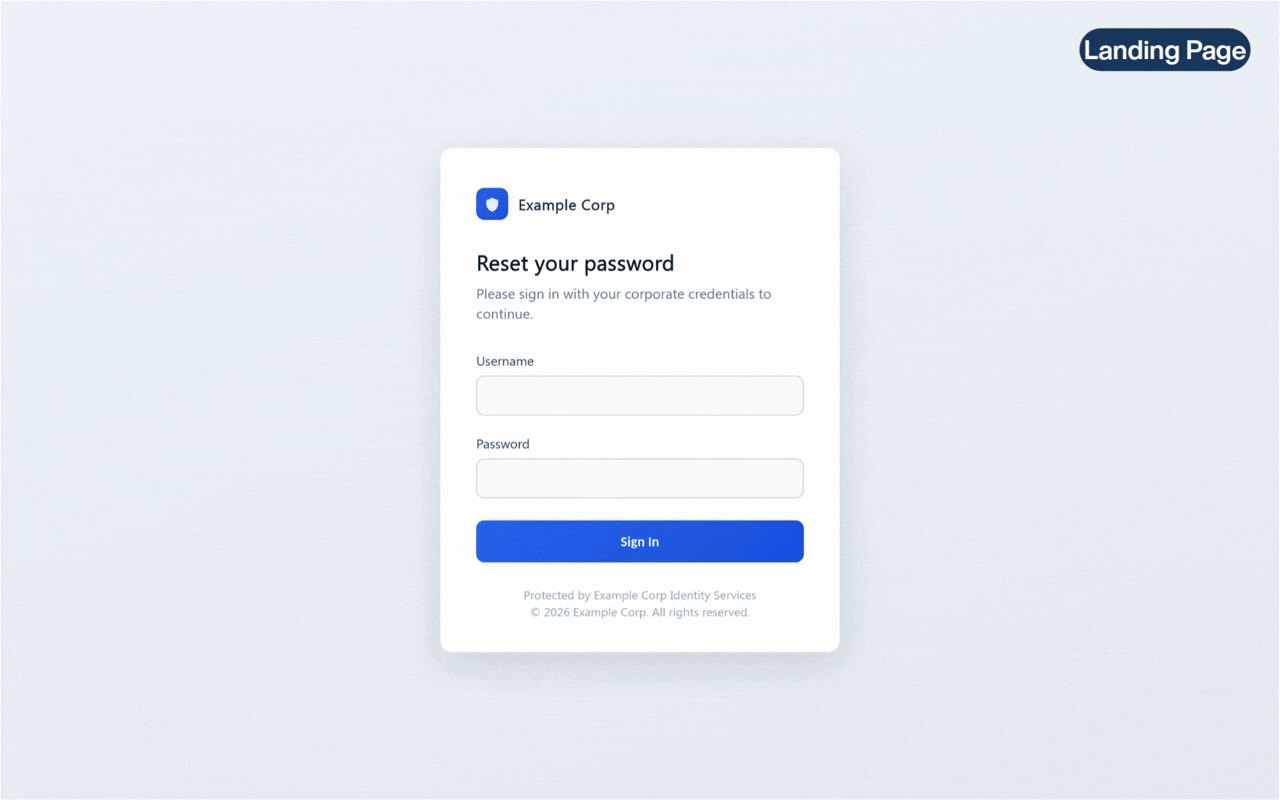
Gophish is an open-source phishing toolkit designed for businesses and penetration testers. It provides the ability to quickly and easily set up and execute phishing engagements and security awareness training — landing pages, email templates, target groups, sending profiles, and per-recipient tracking, all through a single web UI.
Pre-built binaries for this fork are available on the releases page. Alternatively, build from source (see below).
Requires Go 1.26 or above.
git clone https://github.com/raginx/gophish-ng.git
cd gophish-ng
go build
After this, you should have a binary called gophish in the current
directory.
The built frontend assets (static/js/dist/, static/css/dist/) are
checked into git, so this is all you need for a normal build. If you
change anything under static/js/src/ or static/css/, rebuild them
with:
npm install
npm run buildThis fork publishes its own Docker images to the GitHub Container Registry on every release:
docker pull ghcr.io/raginx/gophish-ng:latestConfiguration can be supplied via environment variables instead of
mounting a config.json - see the
Docker installation docs
for the full list of supported variables.
After running the Gophish binary, open a browser to https://localhost:3333
and log in with the default username and password printed in the log
output, e.g.:
time="2020-07-29T01:24:08Z" level=info msg="Please login with the username admin and the password 4304d5255378177d"
A phishing campaign is assembled from a few building blocks. Create each one from the sidebar, then tie them together in a campaign:
- Sending Profile the SMTP server the emails are sent through.
- Email Template the email recipients receive. Put the
{{.URL}}variable where the phishing link should go; opens and clicks are tracked for you. - Landing Page where the link leads, and optionally where submitted credentials are captured.
- Users & Groups the recipients to target.
- Campaign pick a template, landing page, sending profile, and group, set the phishing URL, and launch. Follow live results on the campaign's results page, and open its Report for the aggregate, printable summary (including the NIST Phish Scale difficulty and the program trend).
Don't want to write the first template from scratch? This fork ships a
starter Content Pack with three example phishing emails and matching
landing pages for a fictional company, Hooked Media Co. Go to
Content Packs → Import, choose static/content-packs/starter.json (it's
included in the release archive and the Docker image), and import it. You'll
get ready-made Email Templates and Landing Pages, leaving only a Sending
Profile and a Group to add before launching.
The full user guide is available at raginx.github.io/gophish-ng.
Found a bug specific to this fork? Please file an issue here.
reinhard [at] westerholt [dot] me
MIT, same as upstream Gophish — see LICENSE for the full text.