Fix masked Netlify OAuth secret validation - #5049
Conversation


…y-prebuilt-workflow.test.ts (2 files)

|
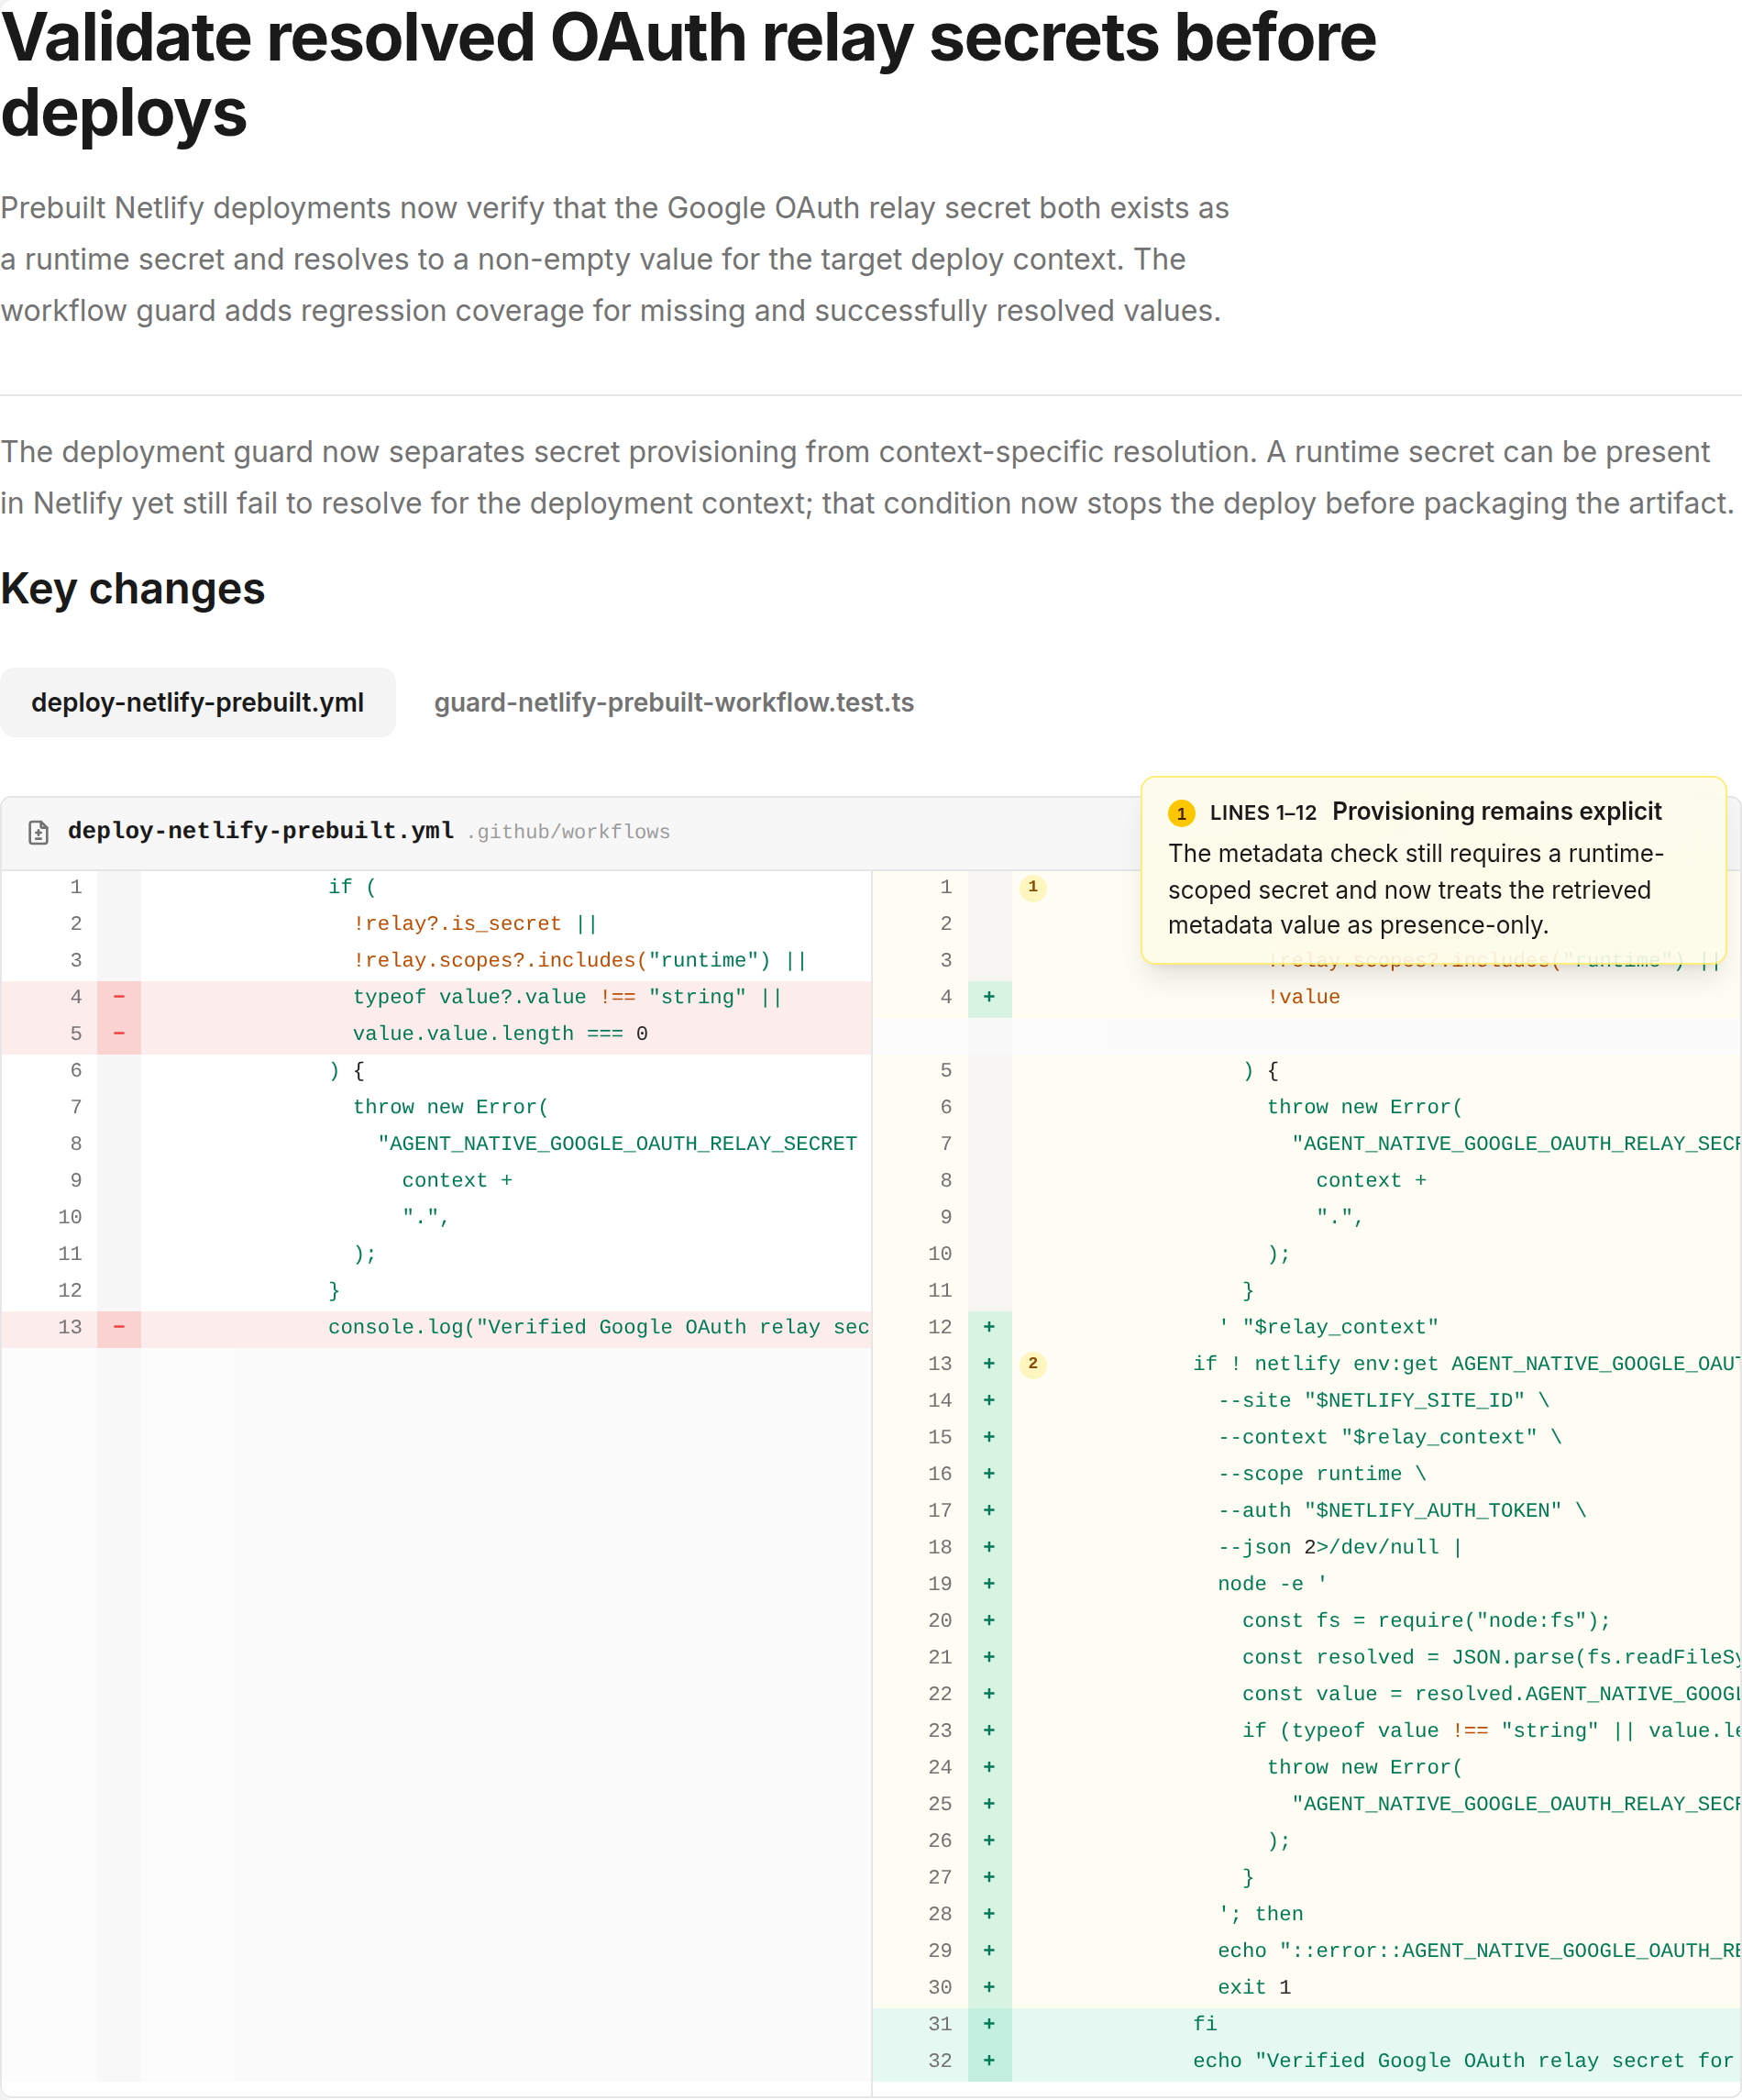
Here's a visual recap of what changed: Open the full interactive recap |

This comment was marked as outdated.
This comment was marked as outdated.
Sorry, something went wrong.
…y-prebuilt-workflow.test.ts (2 files)

There was a problem hiding this comment.
Builder reviewed your changes — looks good ✅
Review Details
Incremental Code Review Summary
The latest commit addresses the previously reported secret-validation gap. The workflow now pipes the suppressed netlify env:get --json output into a Node resolver that explicitly requires a non-empty AGENT_NATIVE_GOOGLE_OAUTH_RELAY_SECRET; failures from the CLI, invalid JSON, {}, or a missing/empty field propagate through the pipeline and fail the deployment. The metadata validation still avoids relying on Netlify's masked value, and the production Google credential definitions remain untouched.
Two independent incremental reviews found no new actionable issues. The added regression coverage exercises both the empty {} response and a valid resolved secret. The previously reported review comment was verified fixed and resolved before this review.
Risk assessment: Standard deployment/secret-validation risk.
✅ No new high- or medium-severity findings.
✅ Secret values remain suppressed from workflow output.
✅ Workflow test coverage now covers the zero-exit empty response.
🧪 Browser testing: Skipped — PR only modifies backend/config/docs, no UI impact


1 participant

Netlify masks secret values in getEnvVars responses, so the Beta production guard was rejecting a provisioned relay secret.
Use API metadata for context/secret/runtime-scope validation, then resolve the value through
netlify env:getwithout emitting it. Keep the existing production Google credentials untouched.